The short answer is no.
For contractors handling Federal Contract Information or Controlled Unclassified Information (CUI), confusing an administrative adjustment with regulatory relief is a costly mistake. As an authorized C3PAO, IBSS evaluates contractor compliance objectively against DoD standards.
Here are the primary misconceptions surrounding recent CMMC pauses, what remains legally binding, and the role of independent third-party assessments.
Misconception 1: “A pause means NIST SP 800-171 is no longer enforced.”
The Reality: The baseline technical requirements have not changed.
CMMC is the enforcement and verification mechanism; it is not the security standard itself. The underlying requirement to protect CUI is governed by DFARS clause 252.204-7012, which has been in defense contracts for years.
Regardless of phase shifts or procedural reviews at the program level:
- DFARS 252.204-7012 remains fully in effect.
- Contractors handling CUI are contractually obligated to implement the 110 requirement controls of NIST SP 800-171.
- Self-assessment scores and affirmations must continue to be submitted and maintained in the Supplier Performance Risk System (SPRS).
Contracting officers and prime contractors still evaluate cybersecurity standing during source selection and award determinations. Assuming a program timeline adjustment relaxes, basic safeguarding duties exposes contractors to non-compliance disputes and potential liability under the Department of Justice’s Civil Cyber-Fraud Initiative.
Misconception 2: “C3PAO certifications are halted or invalid during program reviews.”
The Reality: Independent third-party assessments remain fully authorized and legally valid.
A common point of confusion is whether authorized C3PAOs can still conduct assessments while milestones are reviewed. The Cyber AB and DoD have established that authorized C3PAOs maintain full authority to execute Level 2 assessments and submit verified results into the Enterprise Mission Assurance Support Service (eMASS) for publication into SPRS.
Furthermore:
- Existing CMMC certificates remain valid.
- Voluntary third-party assessments remain available for organizations seeking to validate their posture ahead of hard deadlines.
- A verified C3PAO assessment provides unambiguous proof of NIST SP 800-171 compliance, relieving prime contractors of the uncertainty tied to self-attestation.
Misconception 3: “Waiting for absolute finality is the most cost-effective strategy.”
The Reality: Backlogs do not disappear. Instead, they compress.
When administrative deadlines shift, many organizations freeze compliance activities until new target dates are published. However, implementing and sustaining operational cybersecurity practices is not an overnight endeavor.
With a finite number of authorized C3PAOs and qualified lead assessors across the nation, waiting until a deadline is reinstated typically results in scheduling bottlenecks that can directly jeopardize award eligibility. Organizations that use the current environment to finalize their posture and achieve voluntary certification enter competitive procurements with an unassailable differentiator: verified, audit-ready compliance.
Understanding the C3PAO Role
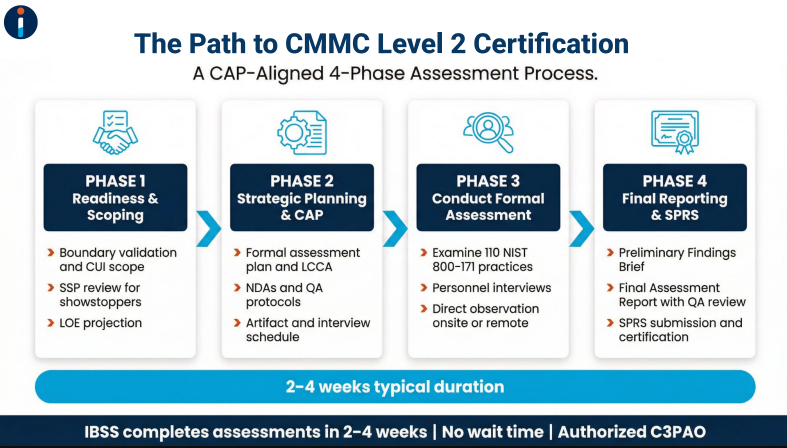
To maintain the integrity of the defense supply chain, the division between assessment and consulting is strictly enforced. As an authorized C3PAO, IBSS does not provide advisory services, readiness preparation, or gap remediation. Our function is strictly independent:
- Objective Evaluation: We conduct formal CMMC Level 2 assessments to examine, interview, and test controls against the NIST SP 800-171 framework.
- Independent Verification: We provide unbiased validation of an organization’s security posture.
- Official Certification: Upon successful evaluation, we issue assessment findings directly into official DoD tracking systems.
By understanding that compliance requirements remain active and that independent certifications continue uninterrupted, defense contractors can navigate program updates with clarity and avoid operational delays.
To discuss scheduling an independent CMMC Level 2 third-party assessment with the IBSS assessor team, contact our cybersecurity team.
About IBSS
Since 1992, IBSS, a woman-owned small business, has provided transformational consulting services to the federal defense, civilian, and commercial sectors. Our services include: cybersecurity and enterprise information technology (including CMMC Level 2 Assessments), environmental science and engineering (including oceans, coasts, weather, and satellite), and professional management services. IBSS is committed to service excellence – to our clients, employees, partners, and the global community as a whole. We proactively create value through science, technology, innovation, agility, and adaptability.